Last Updated on 28/01/2022 by Ulka
A new, complex phishing assault has been noticed conveying the AsyncRAT trojan as a component of a malware crusade that is accepted to have been initiated in September 2021.
“Through a basic email phishing strategy with an HTML connection, danger aggressors are conveying AsyncRAT (a remote access trojan) intended to remotely screen and control its tainted PCs through a protected, encoded association,” Michael Dereviashkin, a security specialist at big business break anticipation firm Morphisec, said in a report.
The interruptions start with an email message containing a HTML connection that is veiled as a request affirmation receipt (e.g., Receipt-<digits>.html). Opening the bait document diverts the message beneficiary to a page inciting the client to save an ISO record.
However, dissimilar to different assaults that course the casualty to a phishing space set up unequivocally for downloading the following stage malware, the most recent RAT crusade cunningly utilizes JavaScript to locally make the ISO record from a Base64-encoded string and copy the download interaction.
“The ISO download isn’t produced from a distant server yet from inside the casualty’s program by a JavaScript code that is implanted inside the HTML receipt record,” Dereviashkin clarified.
At the point when the casualty opens the ISO record, it is naturally mounted as a DVD Drive on the Windows have and incorporates either a .BAT or a .VBS document, which proceeds with the disease chain to recover a next-stage part by means of a PowerShell order execution.
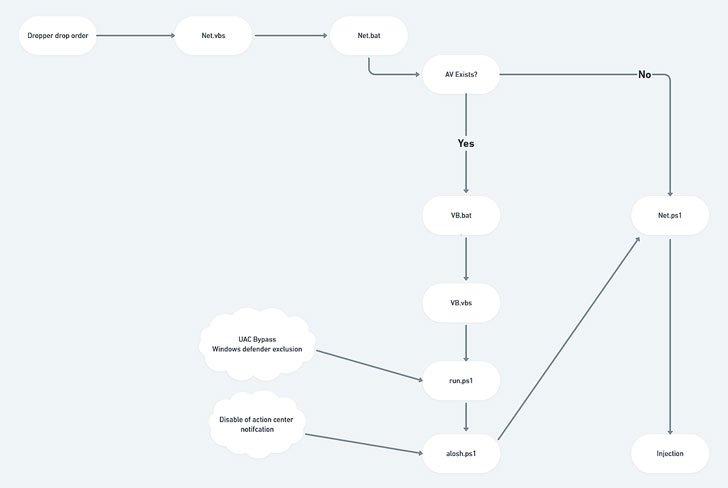
This outcome in the execution of a .NET module in-memory that therefore goes about as a dropper for three records – one going about as a trigger for the following – to at long last convey AsyncRAT as the last payload, while additionally checking for antivirus programming and setting up Windows Defender avoidances.
Rodents, for example, AsyncRAT are commonly used to produce a remote connection between a dangerous entertainer and a casualty gadget, take data, and direct observation through receivers and cameras. They give a variety of cutting edge capacities that enable the assailants to completely screen and control the compromised machines.
Morphisec additionally brought up the mission’s high-level strategies, which it said permitted the malware to fall through practically undetected by most antimalware motors notwithstanding the activity being active for near five months.